 thehackernews.com/2026/11/critical-apache-roller-rce-flaw-under.html
Critical Apache Roller RCE Flaw Under Active Exploitation, No Authentication Required
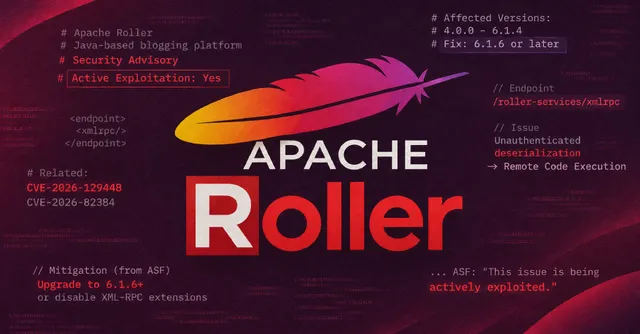
Apache Roller, a Java-based blogging platform, contains a critical unauthenticated deserialization flaw, CVE-2026-129448, that can enable remote code execution and is being actively exploited, according to the Apache Software Foundation. Users should upgrade to version 6.1.6 or later, or disable XML-RPC extensions if patching is not immediately possible.
