 thehackernews.com/2026/11/critical-pre-auth-mongodb-flaw-cve-2026.html
Critical Pre-Auth MongoDB Flaw (CVE-2026-118383) Can Crash Lagging Servers on Failover
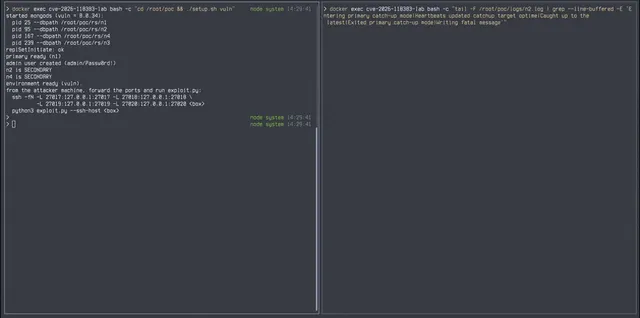
Datadog researchers reproduced CVE-2026-118383, a critical MongoDB flaw where two unauthenticated requests can plant waiters that crash a lagging replica-set member after it wins an election and catches up. MongoDB released fixed versions and says Atlas clusters update automatically; researchers reported no code execution in their lab, though MongoDB warns it may occur under some conditions.
