 thehackernews.com/2026/11/hackers-exploit-critical-xen-orchestra.html
Hackers Exploit Critical Xen Orchestra Auth Bypass Flaw to Gain Admin Access
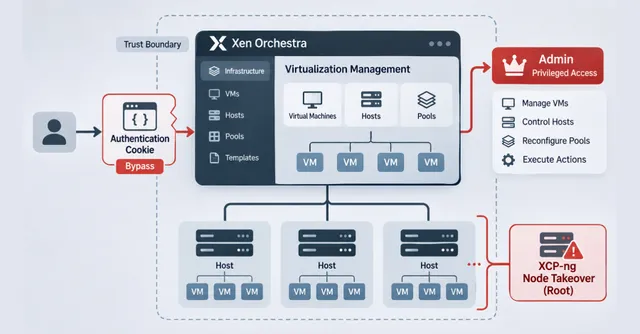
Vates VMS warned that a critical Xen Orchestra authentication bypass, tracked as VSA-2026-062 and without a CVE identifier yet, is being actively exploited. It can let attackers act with Admin privileges and lead to root takeover of managed XCP-ng nodes; Vates lists fixes in Xen Orchestra 6.9.1 and 6.10.0 and xo-server 5.211.2 and 5.213.1.
